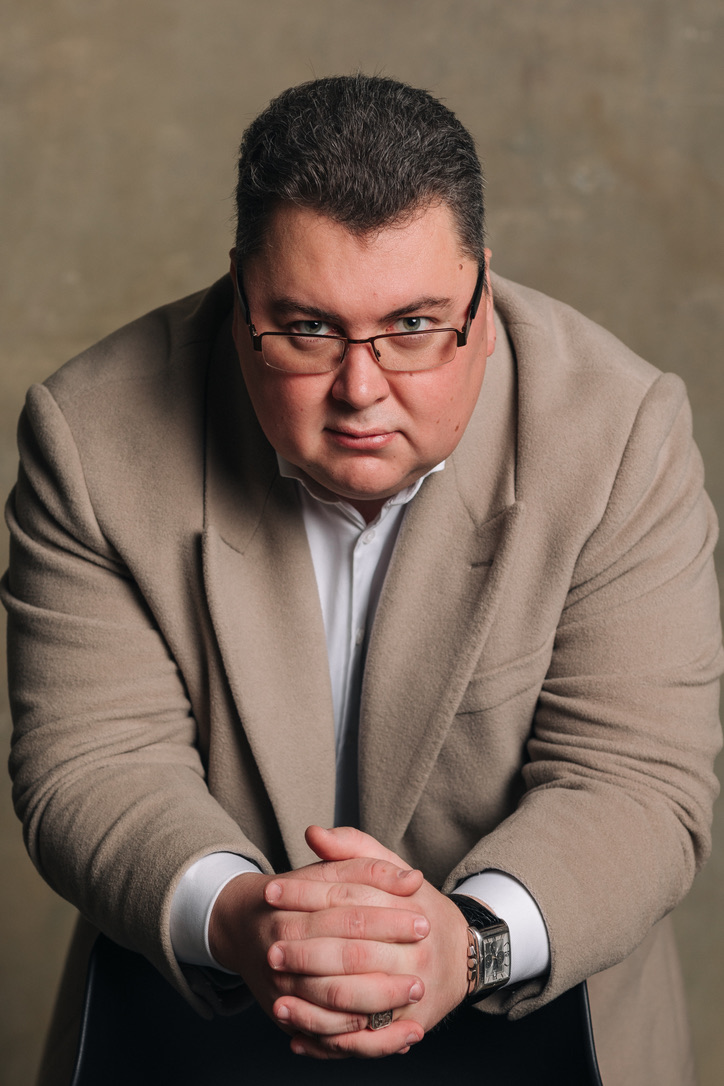
Artem Izbaenkov is a cybersecurity expert, a United Nations cybersecurity consultant and Product Director of Solar Space at Solar Group. His work focuses on DDoS protection, bot mitigation and web application security. He is a co-inventor of Russian patent No. 2851682, the author of a DDoS defense guide and a contributing author of a digital security textbook for secondary school students.
Artem Izbaenkov. Photograph from his personal archive.
BACKGROUND
Experience and contribution.
Artem Izbaenkov works at the intersection of cybersecurity, product management and business development. His areas of expertise include digital service resilience, DDoS protection, bot mitigation, web application and API security, and the use of artificial intelligence in cybersecurity.
He is Product Director of Solar Space at Solar Group and a United Nations cybersecurity consultant. He is a board member of ARSIB and a member of ROCIT and ISDEF. His earlier experience includes leading Servicepipe and developing the cybersecurity business at EdgeCenter. He speaks at industry conferences, takes part in expert discussions and provides media commentary on digital threats.
He is a co-inventor of the web traffic classification method covered by Russian patent No. 2851682. The patent holder is Solar Security JSC. He is the author of a practical DDoS defense guide and a contributing author of Digital Security for Grades 10–11, published by Prosveshcheniye.
Through his work with ARSIB, he helps organize Capture the Flag competitions and the Russian CTF Cup. He supports cybersecurity education and shares practical experience with emerging professionals.
He is married and has three children. His son Andrey is a game designer, and his daughter is a figure skater. His wife serves in the Main Directorate of EMERCOM of Russia for the Moscow Region and holds the rank of major.
English summaries of three published materials. The original materials are in Russian; each card identifies Artem’s role.
Anti-Malware.ru
Article by Artem Izbaenkov
The dark side of AI: threats and protection
An introduction to the use of AI in phishing and automated attacks, and to a layered defence combining technical controls, software updates and employee awareness.
A discussion of protection deployment, traffic filtering and coordination with a provider during an attack. Useful context for teams responsible for the availability of digital services.
Protecting websites and applications in smaller businesses
An interview about security priorities for small and medium-sized businesses, including automated bots, applications and APIs. A starting point for connecting technical risks to business decisions.
Original guides by Artem Izbaenkov, with short English summaries to help you choose a starting point. The guides, worksheets and source notes are in Russian.
Original guide · Russian
Original guide by Artem Izbaenkov
Read protection reviews with care
Use the Atlas methodology to scope a documentary review: identify the product, deployment and evidence date, then separate documented features, vendor claims, observations, measurements and unknowns. Fourteen common criteria and cohort-specific questions guide the reading. This framework does not rank products or demonstrate tested effectiveness.
Start with one API operation and its intended result. Map the expected clients, permitted actions, open questions and responsible people before discussing bot controls. A fictional example of checking product availability and a printable or editable worksheet help structure that conversation. Traffic classification alone does not establish permission, identity or API security.
When a service becomes unavailable, record the affected user task and the limits of each observation. Keep facts, hypotheses and actions on separate timeline tracks, and state what would change your confidence. The evidence card helps document execution, verification and rollback conditions. Recovery after a change does not prove its cause.
Credit portraits to Artem Izbaenkov’s personal archive and preserve their proportions. Portraits in the press kit may be used in editorial coverage about Artem and announcements of events featuring him. Please get in touch about other uses. Event photographs have their own credits and usage context.
LET’S TALK
Have a topic in mind?
For a talk, interview or professional collaboration, share the topic, audience, format and timing.